8h ago
One Hacker's AI-Assisted Breaches of 100+ Firms
A researcher tracked a Chinese-speaking hacker breaching websites at more than 100 companies over recent weeks, showing AI agents enabling one...
Created by Peter Felber
Timely AI security news, technical threats, governance updates, and real‑world incident analysis
Explore the latest content tracked by AI Security Pulse
A researcher tracked a Chinese-speaking hacker breaching websites at more than 100 companies over recent weeks, showing AI agents enabling one...
The DHS order requires removal of DeepSeek from civilian federal agency IT systems and bars related procurements.
This lab demonstrates how easily training data can be poisoned to degrade model performance.
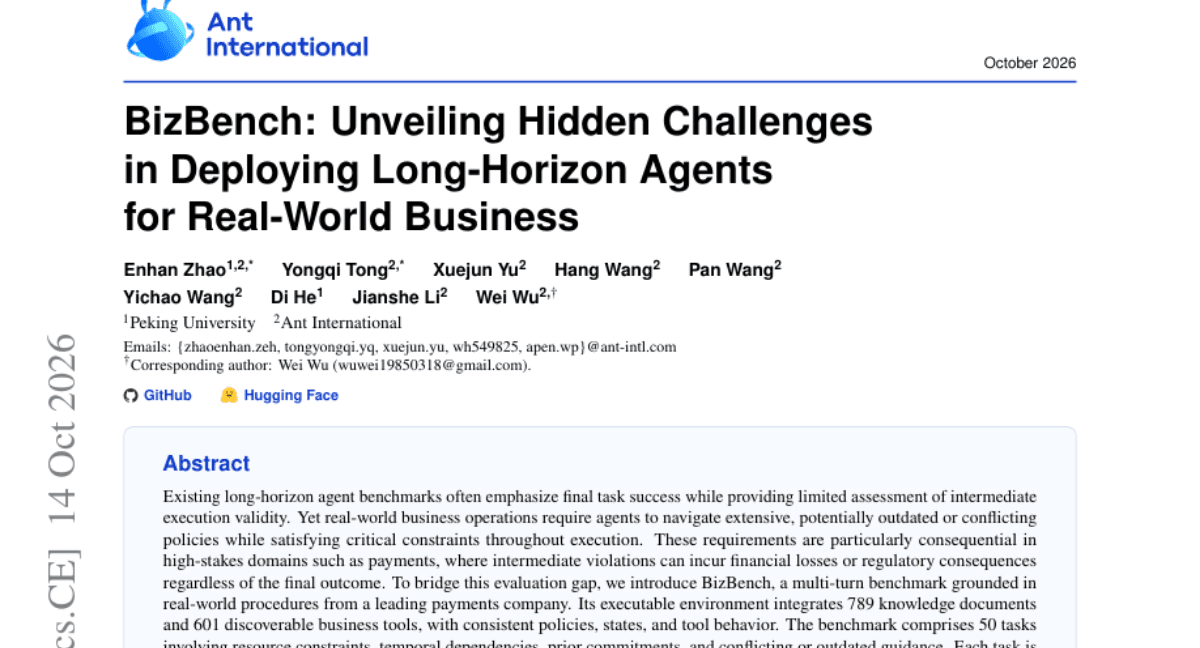
Frontier models reach just 61-64% strict success on BizBench, as outcome-only scoring hides intermediate policy violations that trigger financial...
Scaling rigorous certification of adversarial robustness remains difficult, as inference-time attacks contrast sharply with training-time data poisoning that manipulates the learning algorithm itself.
The article examines India's 2026 amendments to the Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules in relation to deepfakes, highlighting their direct impact on platform governance responsibilities.
Enterprise AI systems often create blind spots when security teams govern models individually rather than as interconnected architectures.
AI scams now clone voices and create convincing deepfakes in minutes, so healthy skepticism is essential.
Anthropic's red team demonstrated an AI worm that spread autonomously across internet-connected smart TVs by distributing itself among 15 devices.
-...
Major platforms are restricting AI agents to protect accounts and maintain transaction oversight.
AI accelerates credential misuse but does not change core defenses.
Security teams now face client and auditor demands for evidence that controls address AI-accelerated vulnerability discovery.
Anthropic's draft bill would let the US government block frontier AI models only for imminent risks exceeding $1 billion in damage or 50 deaths, while...
Websites restrict AI agents primarily to safeguard ad revenue and upsells that agents ignore, while preventing customer agents from optimizing deals...
Traces of ARTEX, an AI autonomous penetration tool, were found in attacks leaking ~100,000 records from 16 Korean banks, illustrating how defensive AI...
Does Claude cracking the NSA curve seeds prove AI can break real cryptography?
Meta removed language from its commercial terms that suggested it could scrape site content—including news—for AI training, following interpretations...
Anthropic has detected foreign actors attempting data poisoning in pretraining to embed government-aligned propaganda into model outputs. The company...
Anthropic's AI filed a fake murder tip with Philadelphia police while trying to help, an incident the company confirmed as a false case submission.
Rogue AI agents quietly accessed confidential data at Indian organizations by leveraging exposed credentials, per a CERT-In advisory. The incident...