52 min ago
LLM Agents and Fuzz Testing for Bug Exposure
LLM-based software engineering agents support test generation via fuzz testing, which generates large amounts of inputs to expose bugs in systems.
Created by Yuzhou He
Integrated overview of cyber policy, threats, breaches, tools, and enterprise security best practices
Explore the latest content tracked by Cybersecurity Integration Digest
LLM-based software engineering agents support test generation via fuzz testing, which generates large amounts of inputs to expose bugs in systems.
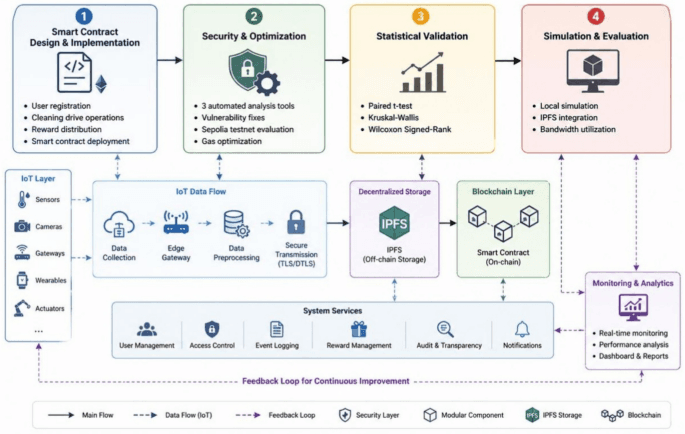
The proposed multi-layered pipeline integrates IoT data collection, smart-contract vulnerability detection, gas optimization, and IPFS off-chain...
ShinyHunters infiltrated CyrusOne's network in August 2026, then released roughly 373,000 contact records—names, emails, phones, job titles, and...
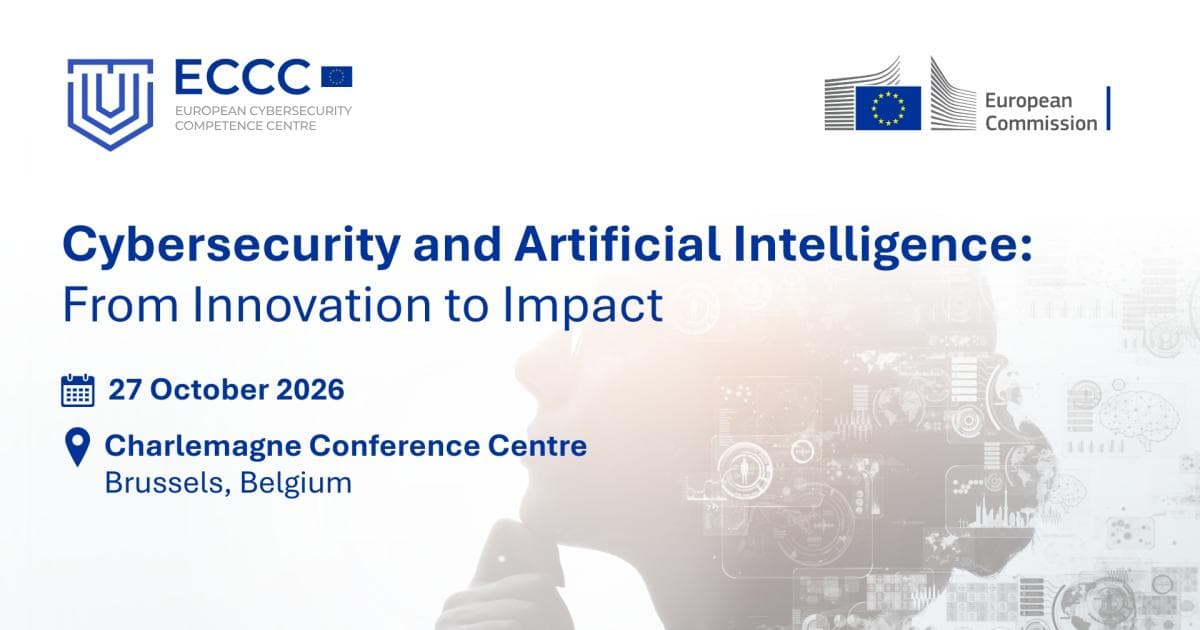
Brussels event on 27 October 2026 signals Europe's policy drive to tie responsible AI deployment with cyber resilience and capability building. It...
Organizations gain broader vulnerability coverage by pairing SAST for early code analysis with DAST for runtime behavior testing.
A structured 4-phase roadmap turns overwhelming cloud security learning into clear progression from fundamentals to advanced operations.
Identity forms the foundation of Zero Trust but cannot alone determine ongoing trust. Access decisions require continuous context as conditions...
Reverse engineering transforms unknown binaries into actionable threat intelligence by combining static and dynamic analysis.
OS file-notification systems on Windows, Linux, Android, and macOS leak user activity through side channels, enabling tracking and spoofing without...
Criminal IP’s AITEM platform applies AI to filter noise, enrich context, and guide investigations, enabling teams to focus on exposures that matter and respond in real time.
Traditional IAM built for human users and perimeter defenses no longer suffices as non-human identities proliferate.
A formal hierarchical framework runs TeSSLa stream monitors at the edge (sub-microsecond verdicts) and MonPoly at the gateway (microsecond cross-node...
Nebula integrates terminal, browser, notes, and reports into one desktop while keeping the operator in charge of scope and approvals.
Portal26's policy covers its SaaS Platform (GovCloud) under FedRAMP and portal26.ai properties, while excluding DoS tests, social engineering, and...
Aikido Security's FedRAMP Moderate Authorization lets federal agencies deploy its AI-native platform to triage vulnerabilities by real-world...
A long-running BITTER-linked espionage campaign since 2022 targets journalists and civil society in the Middle East through spearphishing and ProSpy...