August 29, 2026
Container security as a full lifecycle: hermetic builds meet ongoing patching
Hermetic builds eliminate network access during image creation by prefetching pinned dependencies into local caches, delivering reproducibility and...
Created by KVNVK (3D)
Deep‑dive Reddit and Twitter tutorials, code snippets, and architecture insights for smart contracts, Web3, SaaS
Explore the latest content tracked by DevTech Deep Dive
Hermetic builds eliminate network access during image creation by prefetching pinned dependencies into local caches, delivering reproducibility and...
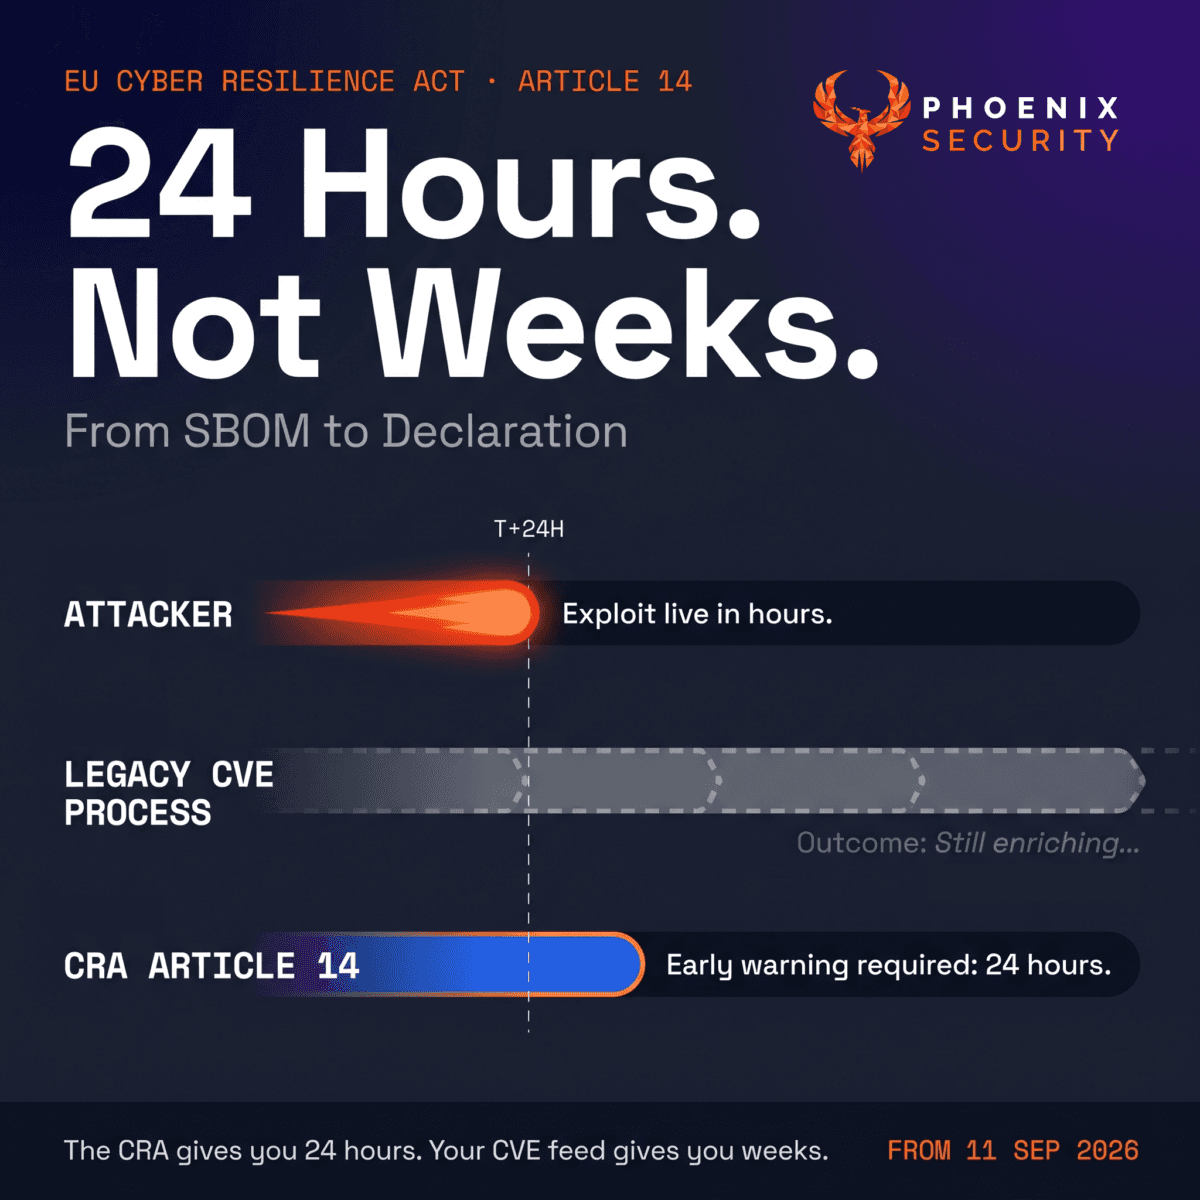
CRA Article 14 turns SBOM generation into an operational pipeline that must deliver attribution and exploitability decisions inside 24 hours.
-...
Teams facing HNDL risks in banking microservices can add quantum resistance today using hybrid patterns instead of waiting for PQC TLS.
A commissioned, ongoing audit by Shielded Labs let Taylor Hornby privately discover the Orchard Action circuit's soundness flaw in the variable-base...
LabVIEW teams in aerospace, medical, and defense must now prove software trustworthiness amid rising threats and regulations.
AI-agent safety requires treating actions as operational control-plane problems, not just model confidence.
Developer environments are the primary target for real AI supply chain attacks today.
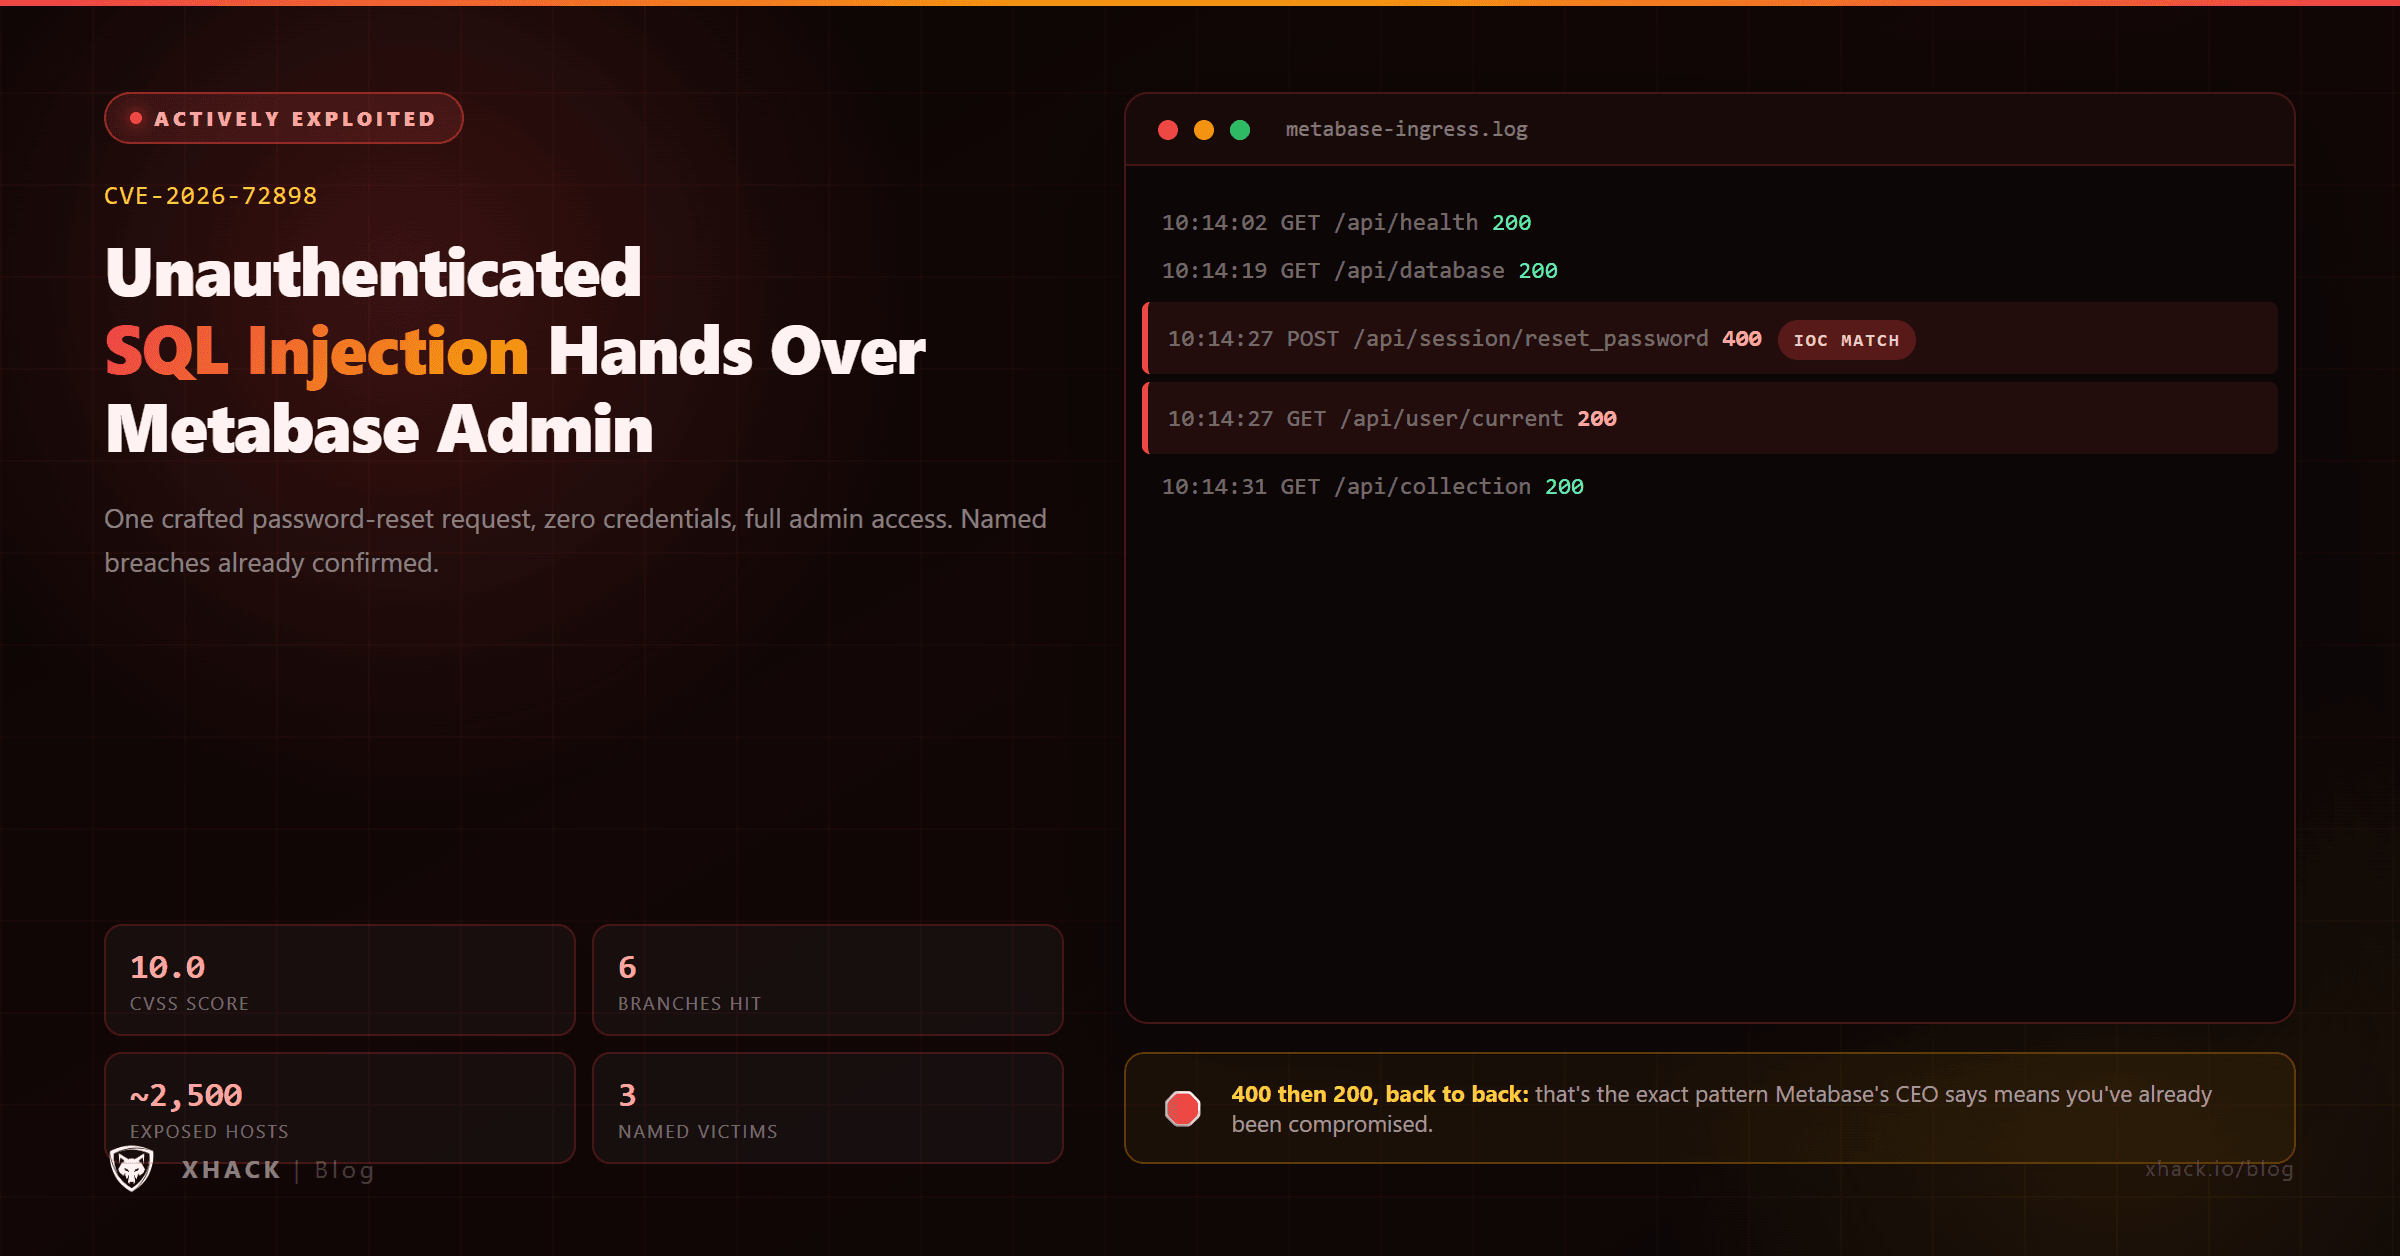
Metabase’s POST /api/session/reset_password endpoint accepted an unexpected user-id field. The HoneySQL query builder compiled it directly as a raw SQL...
Vitest is extracting a standalone browser-side capture primitive so DOM snapshots can be recorded from Node tests or Playwright-driven E2E setups.
-...
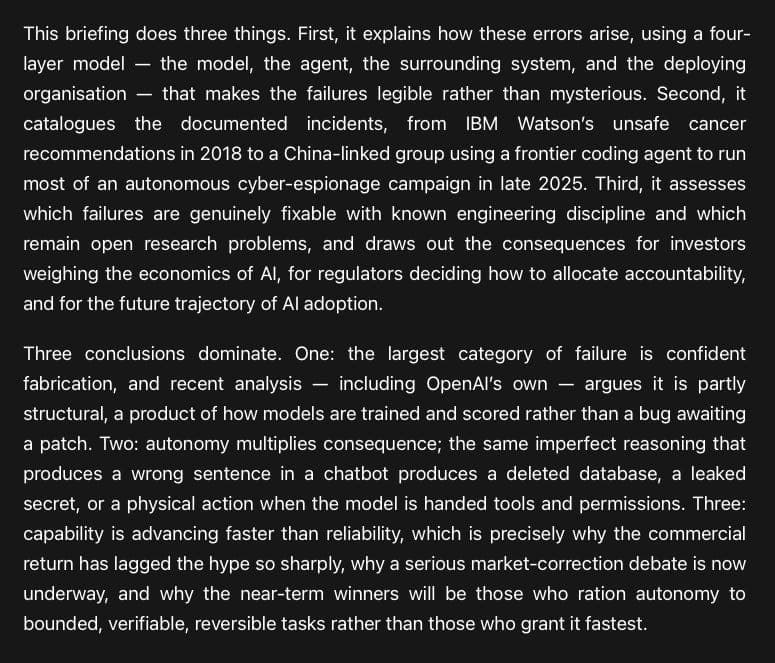
Serious AI failures stem from aligned layers — model, agent, system, organization — not isolated bugs.
XCSSET infects Xcode projects by embedding in build phase scripts that execute on every compile, traveling with source code shared via repos or...
The Pass-the-Passkey exploit chain is embedded in two Microsoft-specific components: Windows 11's platform authenticator logging and Entra ID's server-side mechanisms.
Attackers now target developer tools and CI/CD pipelines directly, as in the ChainDrop worm's memory scraping and self-propagation via npm hooks.
-...
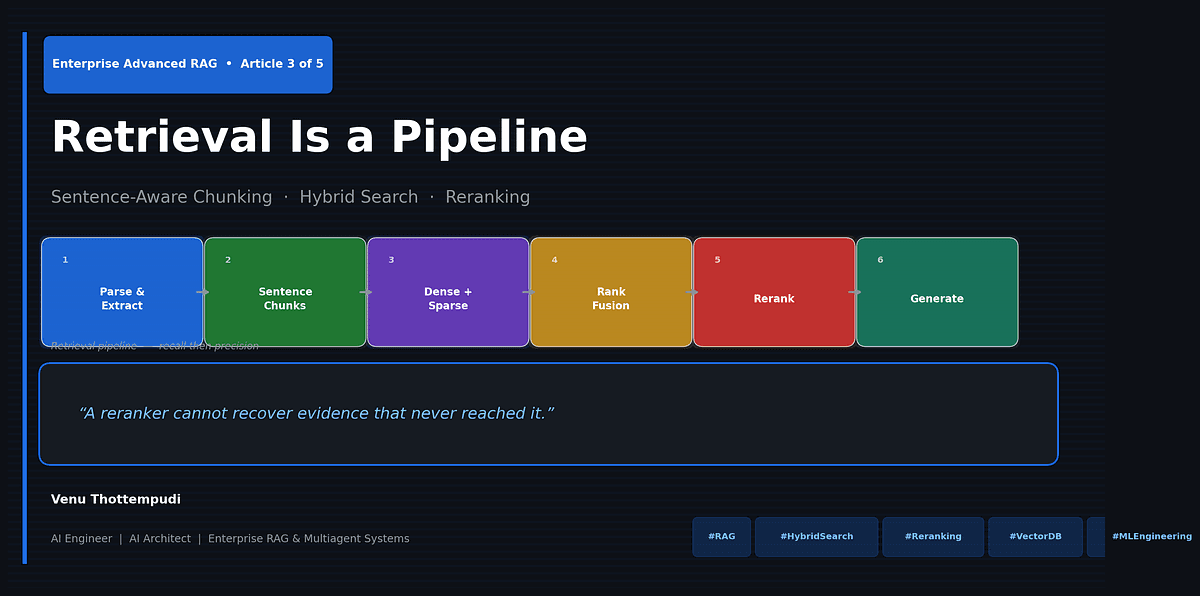
Retrieval failures often trace back to early pipeline stages, not just the reranker.
A holistic quantum migration follows three linked stages.
The attack injected via a single manifest line in compromised arrayref 0.3.10, pulling proc-macro1 (a renamed proc-macro2 copy) whose build script...
The gbnt CLI delivers practical commands to embed Cosign image signing and SBOM generation directly into storage workflows.
gbnt...Air gaps isolate networks but leave every crossing point as the real decision boundary for supply-chain risk.