4h ago
Extended Support as a Stopgap: What the Vendor Pitch Leaves Out
HeroDevs presents its NES offering as a way to buy time, but the page is vendor marketing, so its benefits and costs need weighing:
- Gains:...
Created by CuratorMaster
Cybersecurity news, data breaches, ransomware attacks, hacking incidents, privacy concerns, online security tips, tech security updates
Explore the latest content tracked by Cybersecurity Hacking News
HeroDevs presents its NES offering as a way to buy time, but the page is vendor marketing, so its benefits and costs need weighing:
An independent review traced the exposure to a chain of missed checks.
Affected information types have not been fully disclosed, but the breach reportedly exposed names, Social Security numbers, driver's license numbers,...
The leak exposed workplace records of more than 41,000 DHS employees and contractors. The potential consequences for them are serious:
Gnosis Pay says hackers accessed customer information through the system behind its own branded cards. Its blog post lays out the response:
-...
Japan plans to seek early information about undisclosed software vulnerabilities from US AI developers and other overseas technology companies. The...
Microsoft released Azure Linux 3.0.2022 on Friday night, with its changelog listing more than 470 CVEs. The article ties this volume to AI/LLM-fueled...
The source's headline reports ARTEX abuse targeting the financial sector, but the excerpt doesn't detail that sector-specific targeting, so treat that...
Government cyber incidents in Australia and New Zealand often begin outside hardened departmental cores. The report's research points to school...
Bank phishing now runs like an industry. Threat actors register lookalike domains in bulk, rent ready-made kits, and launch fake sites in minutes. The...
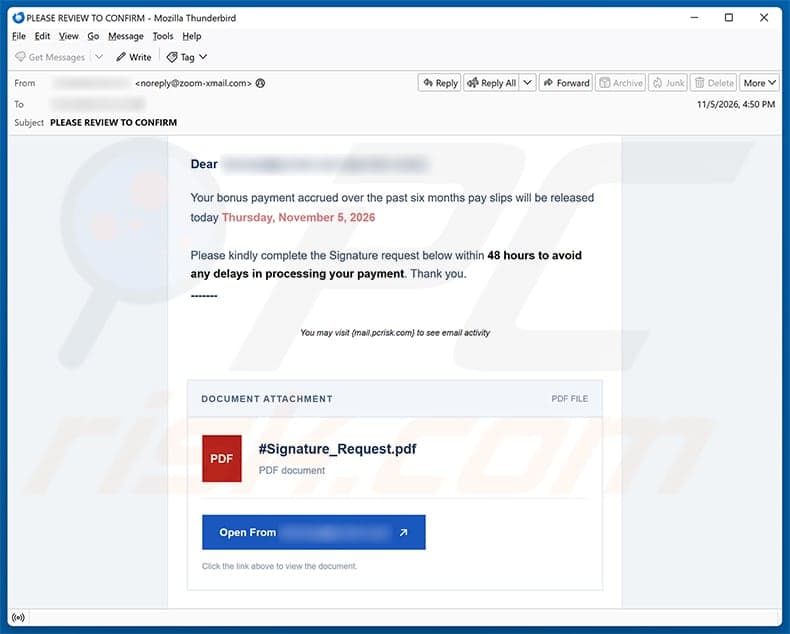
A fake pay bonus is enough to push recipients toward a credential-stealing site. The email falsely claims a bonus is ready for release and sets a...
Chainalysis first said only non-sensitive data was accessed, but it has since widened the disclosure considerably. The exposed data now includes...
Fake texts and emails follow a familiar pattern. The details change, but the request usually stays the same. Scammers may also impersonate government...
Lumma's danger starts with a trick on the user. Its affiliates rely on social engineering, including fake CAPTCHA pages that ask victims to paste a...
Opening a phishing email is usually not the danger. Clicking, opening attachments, or typing in details is. Respond based on what you actually did:
-...
The Chainalysis breach picture changed as the company's account developed:
Aging software keeps adding patching risk, even as most routine updates can wait.
Companies and government agencies rushed last week to patch two critical PHP flaws. The headline describes an AI-found flaw and calls the situation...
Socket is offering a free Certified Patch for GHSA-f3w6-w445-fwh9, a critical Active Storage flaw rated CVSS 9.8. It's available to anyone, not just...