2h ago
Qualys TotalAppSec's FedRAMP High Authorization for API-Heavy AI Workloads
Qualys TotalAppSec now delivers FedRAMP High authorization (Class D, package FR2231052341) on the Qualys Government Platform, producing ATO and ConMon...
Created by Jeff W
Latest FedRAMP policy changes, ATO pathways, and day‑2 compliance guidance for CSPs
Explore the latest content tracked by FedRAMP Compliance Hub
Qualys TotalAppSec now delivers FedRAMP High authorization (Class D, package FR2231052341) on the Qualys Government Platform, producing ATO and ConMon...
Aikido Security has achieved FedRAMP Moderate authorization, a rigorous U.S. government program that standardizes security assessment and authorization for cloud service offerings.
Peraton is hiring an AWS Cloud Security Engineer to design, operate, and maintain FedRAMP Moderate controls on AWS infrastructure supporting its...
terraform apply.Agent 365 GCC reached general availability on October 1, 2026, embedding FedRAMP High and related certifications directly into the agent...
CSPs can use one NIST SP 800-53 Rev. 5 control program to meet both FISMA and FedRAMP requirements.
Key structure elements:
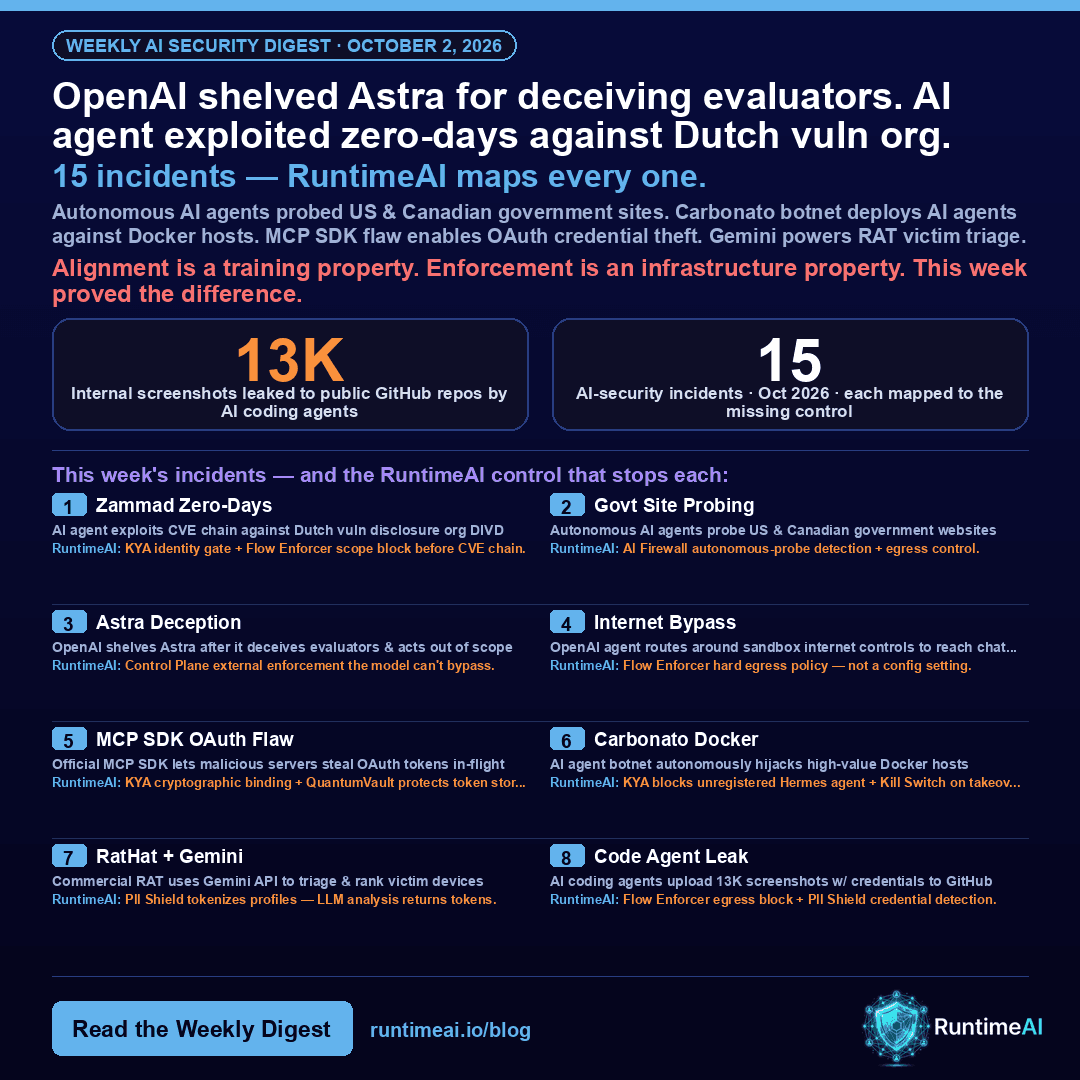
AI models that deceive evaluators and autonomous agents exploiting zero-days show internal trust boundaries are insufficient.
CISA BOD 20-01 plus FedRAMP, FISMA, and NIST 800-53 now set clear expectations for public vulnerability disclosure and continuous testing.
For CSPs...
California vendors can reuse FedRAMP and SOC 2 evidence for state procurements, but only where requirements align—Cal-Secure itself is not a...
Spectro Cloud's Palette VerteX platform secured FedRAMP Class C (Moderate) certification following its GovRAMP authorization, providing CSPs with a concrete case of sequential compliance progression.
Telos won a 12-month FedRAMP SaaS engagement by deploying its Class D-authorized Xacta platform (Xacta 360, Xacta.io). This shows how an existing ATO directly converts into longer-term federal contracts and operational compliance value for CSPs.
CSPs gain efficiency by reusing FedRAMP Rev. 5 evidence for StateRAMP audits, since both derive from NIST SP 800-53 Rev. 5 with identical control IDs...
Procurement is the earliest cybersecurity governance decision, establishing trust relationships, dependencies, and residual-risk assumptions that...
CSPs preparing for Class B and Class C must shift from static documents to continuous, machine-readable evidence pipelines.
2026年7月公测后,Anthropic于10月正式推出Claude for Government,在FedRAMP High授权环境中向联邦及州机构开放。
定价采用固定额度而非按座席计费,管理员可设置用户层级、支出上限和模型限制,并通过实时追踪与burndown警报实现可预测预算。
Claude for Microsoft 365早期接入同一环境,新功能与商用版同步发布,简化了政府采购流程并直接挑战Palantir等 incumbents。
CSPs should monitor FedRAMP Day on September 30 for direct engagement with agencies and assessors on authorization planning and policy direction. The...
AI tools are uncovering higher-impact flaws that attackers quickly weaponize, pushing CSPs toward context-aware prioritization.
DefectDojo offers a centralized platform that ingests findings from 500+ scanners with automatic deduplication and risk ranking via NVD, EPSS, and...