23h ago
Detectify's Agentic Tooling Aims to Make AI Security Findings Verifiable
Detectify has announced Agentic Tooling, which lets organizations' own AI agents investigate suspected vulnerabilities and test whether they can be...

Created by Eduardo Silva
Enterprise DevSecOps news, best practices, compliance, and real‑world case studies
Explore the latest content tracked by Enterprise DevSecOps Digest
Detectify has announced Agentic Tooling, which lets organizations' own AI agents investigate suspected vulnerabilities and test whether they can be...
The article's core point is that Moltbot's safety depends on how you run it. Any agent that reads messages and runs actions can be abused through bad...
This GuruGroup page is a services pitch. It describes a practice pattern of hardened Azure Pipelines, shift-left scanning, Terraform/Bicep, and AKS...
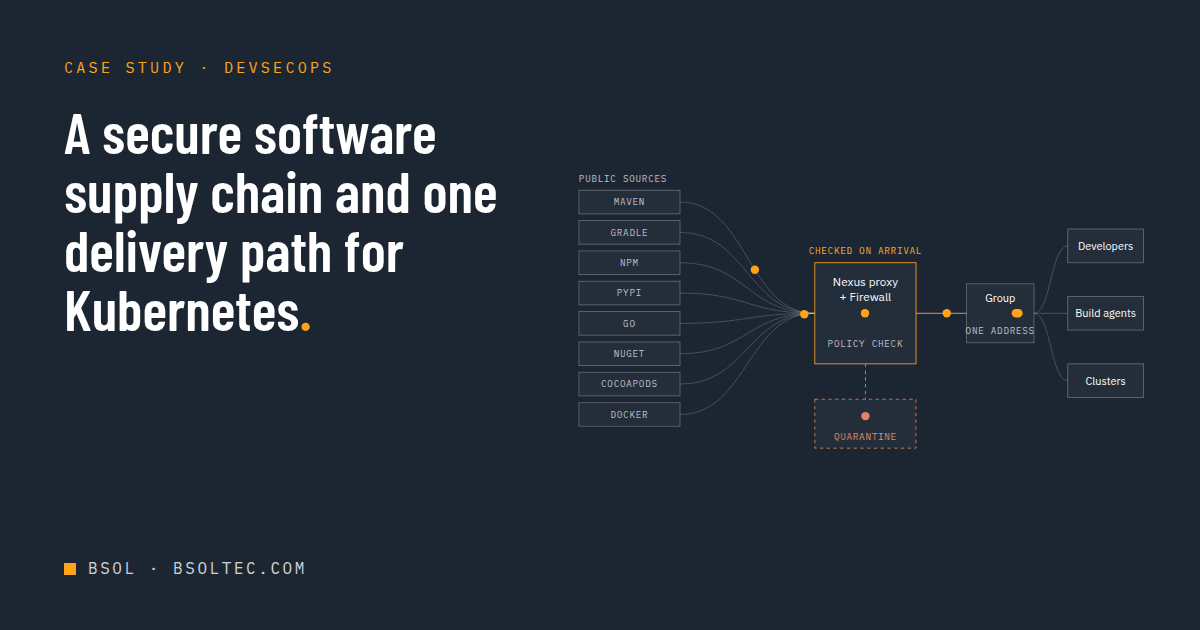
This BSOL case study describes a Hong Kong regulated organisation's path from commit to on-premises Kubernetes, which is designed to run air-gapped....
A practical, beginner-friendly guide covers Kubernetes package management with Helm, including charts, templates, releases, upgrades, and rollbacks....
Microsoft's guidance gives a practical starting structure for hybrid environments:
ERP programs, shared platforms and AI deployments all force the same question: who owns the process, the data and the final decision?
When ownership...
Paxton-Fear calls the champion role often a thankless job, where champions may close fewer tickets than colleagues because they spend time on...
SelectHealth describes provider credentialing going from six months to six days. Its CIO Ryan Brady and Salesforce's Mark Wanish point to connected...
Researchers found exposed credentials tied to nine US healthcare organizations in public GitHub repositories. Some provided access to patient records...
NextLabs says its Enforcer for GitLab, now available, would centralize access rules that teams now embed in individual pipelines. It also targets bots...
Rubrik announced cyber recovery capabilities for Azure DevOps and GitHub, designed to undo attacker changes from air-gapped, immutable backups.
-...
Rubrik says its new cyber recovery capabilities for Azure DevOps and GitHub can undo attacker changes from air-gapped, immutable backups. The workflow...
The best-practices guidance comes down to matching the data source to the job:
Most enterprises already have SoD policies. The harder problem is applying them across fragmented identities. Four practical steps stand out:
This comparison draws on official documentation checked in November 2026, not hands-on benchmarks. Key differences:
The article's trend claims and its vendor positioning deserve separate treatment:
Service account risk usually builds through drift, not one dramatic failure. A practical starting point:
Only 38% of enterprises reach enterprise-grade Kubernetes maturity, even though 61% hold production clusters to the same or higher operational...
Kubernetes breaks the old assumption that storage stays put. Pods can be recreated on a different node in seconds, and a node can fail without...