October 7, 2026
Browser Telemetry Fills SOC Visibility Gaps
Browser credential events often bypass identity, endpoint, and cloud monitoring, leaving shadow IT logins and risky password use invisible to SIEMs....
Created by Futurism Security
Practical updates on cloud SOC operations, tools, and strategies for blue team practitioners
Explore the latest content tracked by Cloud SOC Playbook
Browser credential events often bypass identity, endpoint, and cloud monitoring, leaving shadow IT logins and risky password use invisible to SIEMs....
Static log collection fails against fast campaigns. SOCs must link telemetry, threat context, and response in one loop to cut dwell time.
Key layers...
A SIEM collects logs, correlates events, and fires alerts, but it cannot triage, investigate, or contain threats on its own. For smaller or growing...
Vega positions its agentic platform as the first new operating model since SIEM, turning every alert into a conclusive verdict across data lakes and...
Wiz differentiates with native SIEM/XDR integration, a multicloud detection and response module, the highest G2 rating (4.7/5) among the three, and an agentless architecture.
Network security focuses narrowly on communications while broader SOC operations span endpoints, identities, and cloud—yet attacks cross all...
Three recent releases show AI SOC progress depends on practical foundations, not model hype.
DORA shifts organizations from periodic compliance checks to real-time operational ownership.
Agentic intrusions like the Hugging Face case succeed when four conditions align; break any one and the attack stalls.
SOC teams must actively validate WORKSPACE_ALERTS and WORKSPACE_CHROMEOS completeness rather than relying on "Completed" status and zero parsing errors, which can hide missing alert types and absent device telemetry.
Agentic SOC platforms now emphasize persistent investigation context that carries across alerts, meetings, shifts and handoffs.
SOC automation tools collect, enrich, correlate alerts and act on them so analysts focus on human judgment tasks.
Eight must-have capabilities:
-...
Vega II positions its purpose-built model as the foundation for agentic cyber defense, but SOC teams will demand proof on four fronts before handing...
Exabeam is extending Nova AI investigation and governance features from its cloud New-Scale platform into data-sensitive and on-premises environments...
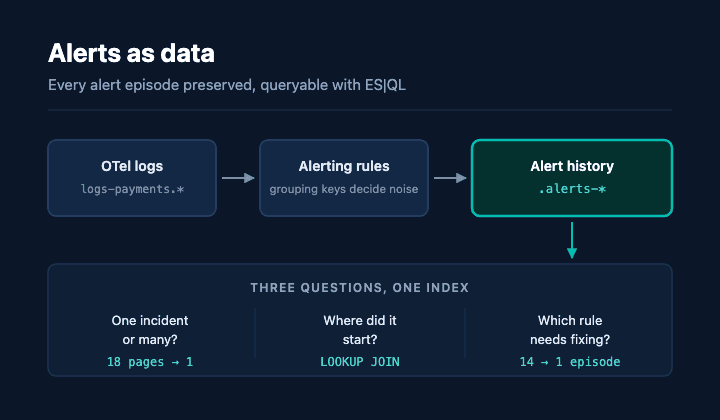
Turn alert tuning into evidence-based engineering by querying preserved alert episodes instead of relying on analyst feedback.
CASB delivers SaaS visibility and policy enforcement but remains a point tool limited to cloud apps.
ADR adds the missing in-application signal to cloud SOC stacks by monitoring real code paths and library calls that WAFs and EDR miss.
LLMOps extends traditional cloud-native DevOps with AI-specific challenges like prompt management, token costs, latency, and observability.
Key tools...