18 min ago
Responding to leaked staff credentials: verify, assess, contain
Treat a credential leak as an identity problem, not a one-off incident.
- Verify exposure: Work out whether the leaked credentials belong to current...

Created by Александр.
Practical OSINT guides for dark‑web market tracking and cyber threat intelligence
Explore the latest content tracked by Dark Web OSINT Hub
Treat a credential leak as an identity problem, not a one-off incident.
The Gentlemen ransomware group added Nvidia to its leak site with a countdown of about 234 hours. Nvidia had not confirmed any compromise, and the...
A critical provider and a low-impact vendor shouldn't get the same review effort. Start by ranking suppliers on service importance, data sensitivity,...
The article argues that outside-in exposure work should include watching where access is sold, not just mapping known assets.
The author's headline warns that your password is probably already on the dark web. Their response was to switch to a password manager that generates...
This SITREP is a headline roundup with no primary sources attached, so treat every lead below as unconfirmed.
Before drawing conclusions, run three quick checks:
Google's Dark Web Report stopped new scans on Jan. 15, and its accounts were deleted on Feb. 16. The replacements fall into two groups:
ESET presents Investigation Lab as a second opinion for suspicious indicators and files. These are vendor claims, so verify them before relying on...
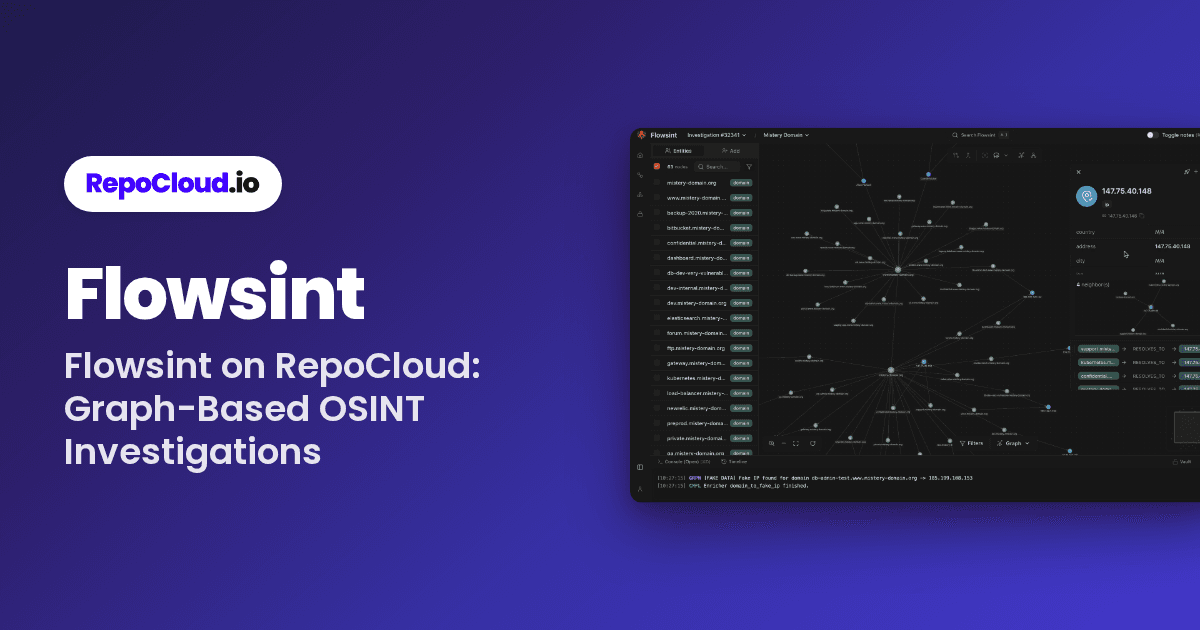
Flowsint combines an interactive entity graph with over 30 enrichers and reusable flows, which could replace scattered terminal output and...
Start free, and pay only if you need structured coursework. The guide labels each option free or paid, and the free path is substantial.
Before comparing any 2026 dark web numbers, check what each one counts. The report uses different windows, selection rules and counting methods, and...
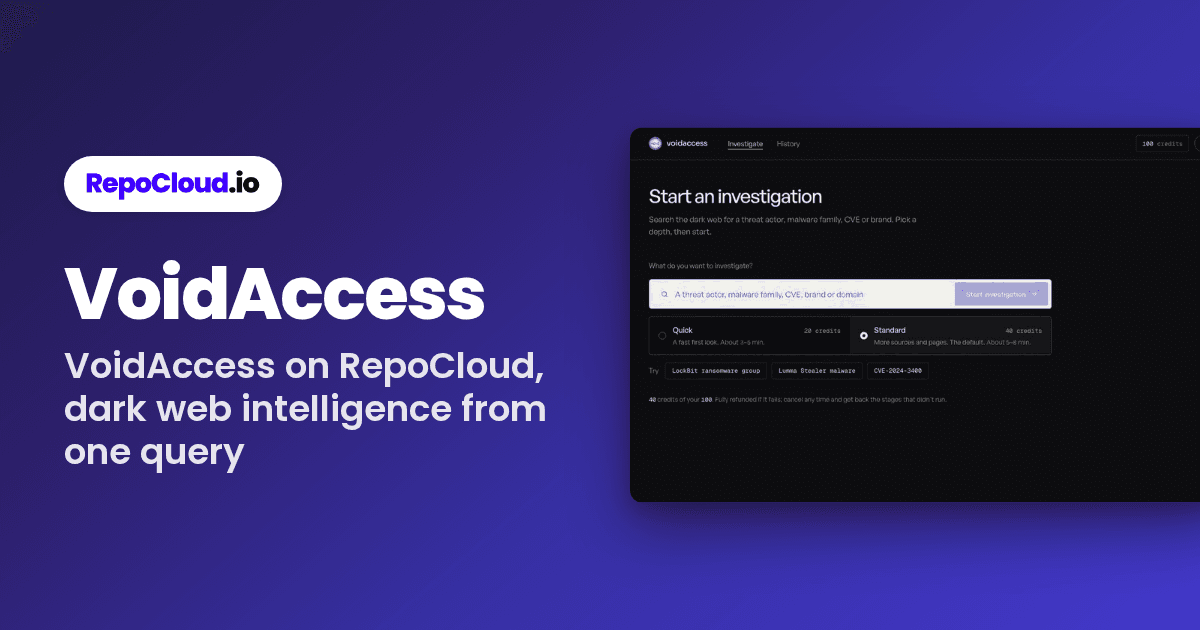
VoidAccess describes itself as a self-hosted dark web OSINT platform that turns one question into a sourced report and indicators. For monitoring and...
The TorBot v4.3.1 write-up describes a tool that collects page titles, hostnames, and link relationships from Tor pages, and exports JSON trees and...
The FBI reports 354 arrests, 5.7 metric tons of drugs, and over $234 million in cash and cryptocurrency, with partners in 13 countries. Europol's...
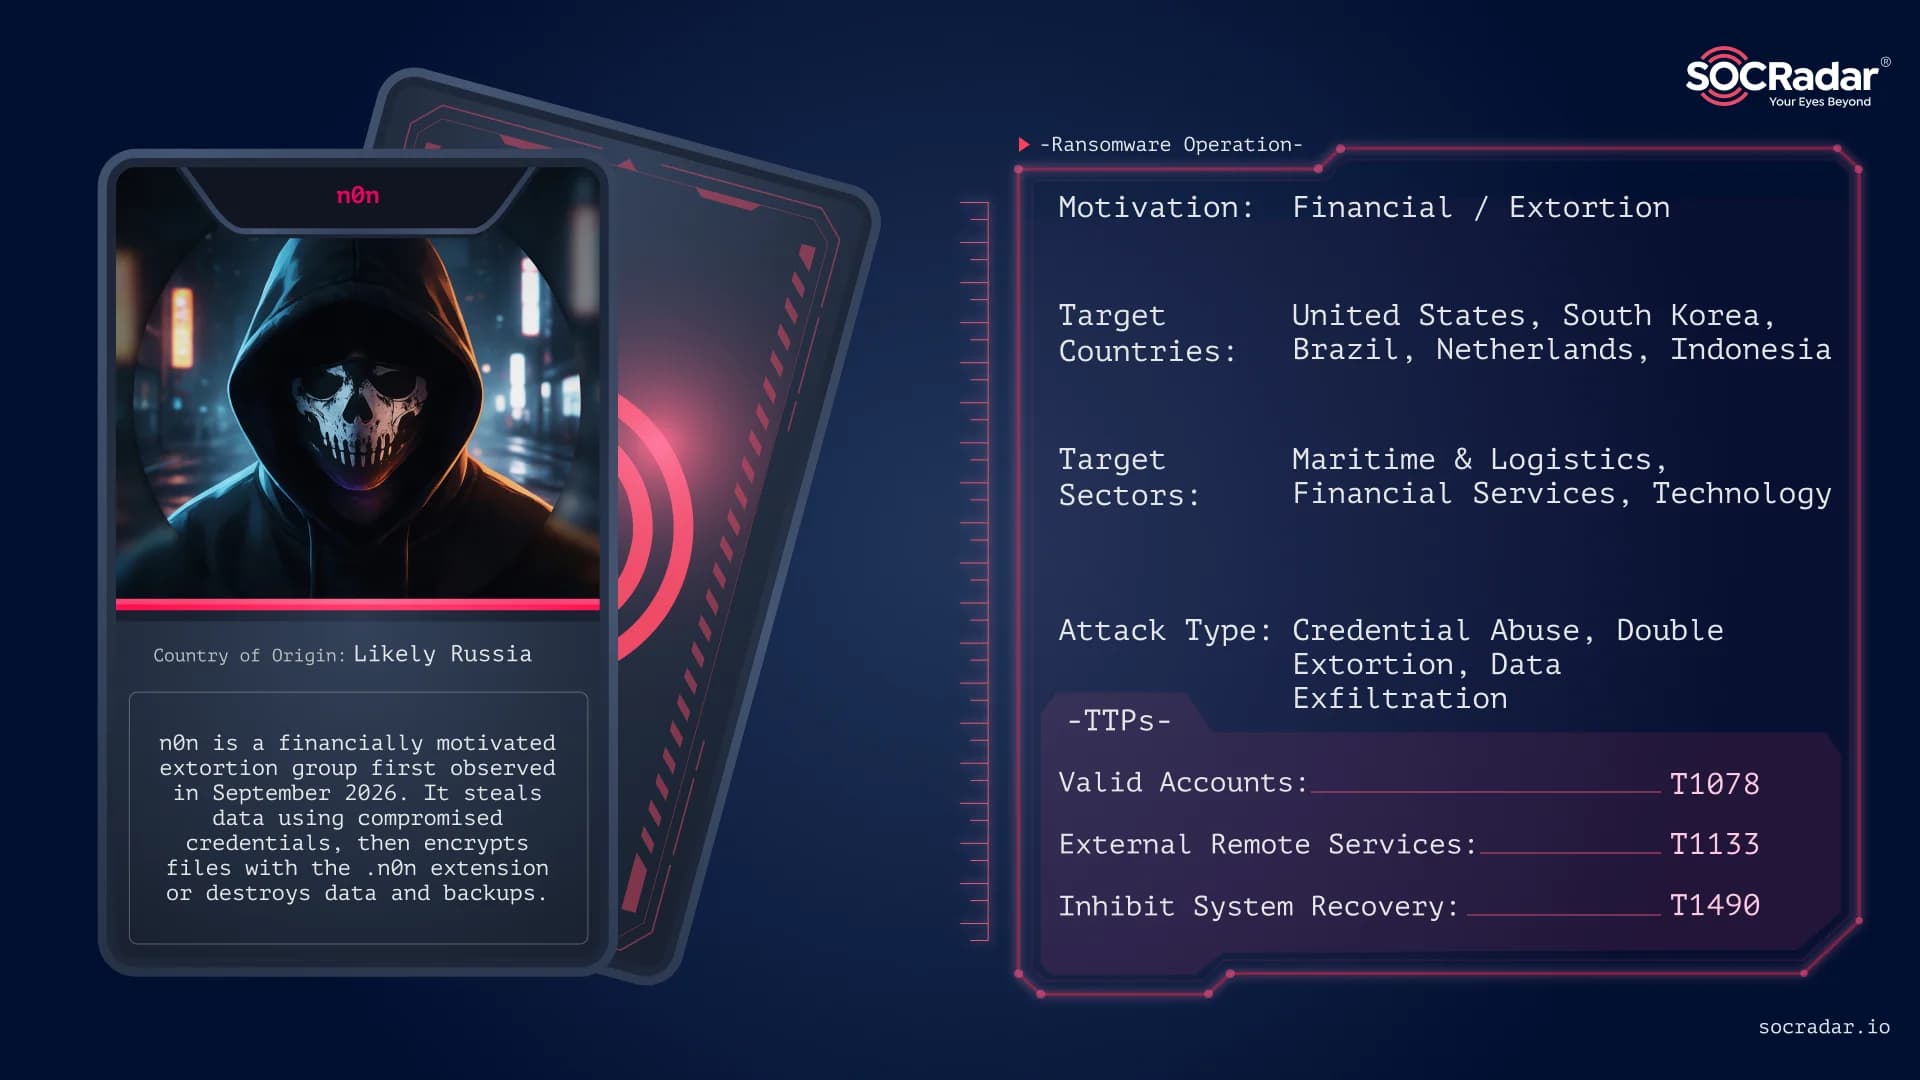
n0n runs a three-stage playbook: data theft and destruction stay private at first, then the victim is listed publicly, then archives are released....
Army CID's RFI points to a shift from reactive to proactive monitoring, using tools beyond keyword searches. The stated needs include:
Before filing anything, work through this checklist:
Build automated pipelines by pairing datacenter proxies with monitoring APIs.
Russian threat actor d4rm3an announced on dark web forum ReHub that Anthropic released its Fable 5 model publicly on June 10. Tracking such posts offers direct signals for AI-related threat monitoring.